
Crypto phishing gives itself away at almost the same point every time: in what the message wants from you. A genuine crypto exchange never asks for your seed phrase, never for your private key and never for the code in your authenticator app. Any email, text message or social media message that asks for one of those three is an attempted fraud, however authentic the sender and the design may look. Everything that follows is the craft of applying that one sentence reliably in daily use.
The occasion for this guide is the situation in late summer 2026. Large data losses at financial and wallet providers mean criminals no longer have to scatter their attempts blindly. They know their targets' names, addresses, phone numbers and in some cases even account balances. A crude mass mailing thereby becomes a personally tailored message that convinces at first glance. The 2026 cybersecurity monitor published by Germany's Federal Office for Information Security puts a figure on how widespread this has become: eleven percent of internet users were affected by an online crime in the previous year alone, phishing accounted for twelve percent of those cases, and one in three of all those affected reports a financial loss.
What separates crypto phishing from ordinary spam
Phishing is the attempt to move you, by means of a forged message, into handing over access credentials or making a payment. The term comes from fishing: the message is the bait and your account is the catch. Spam wants to sell you something and costs you time. Phishing wants your access and costs you money.
In crypto the problem sharpens for a technical reason. A bank transfer can sometimes be recalled, and a direct debit can be reversed as a matter of course. A transaction on a public blockchain is final once it has been confirmed. No institution exists that can take it back, neither at Bitcoin nor at Ethereum. Anyone who has signed the wrong thing once is no longer negotiating, only counting the damage. That is what makes phishing so profitable for criminals in crypto and so expensive for you.
There is a second peculiarity. At a bank, fraudsters need your login credentials. At a self-custodied wallet, your signature on an innocuous-looking approval is often enough. These two routes call for different defences, and this article treats them separately.
Why a data breach at one provider triggers phishing emails in the name of entirely different crypto exchanges
A data breach is the unintended escape of customer data from a provider's systems. What matters to you as a user is which data escaped. If it is copies of identity documents, addresses, phone numbers and transaction histories, then your coins are safe for the moment, because none of that opens a wallet. Such records become dangerous only as raw material for the next step.
Anyone who knows that you are a customer of a crypto provider, what your name is and where you live, can approach you credibly. And they are not limited to the provider where the breach occurred. A list of German crypto customers can be used for any scheme: for a forged security warning from a completely different exchange, for a supposed product recall from a wallet manufacturer, for a call from an invented fraud department. This is the mechanism many people underestimate. A breach at one provider funds the phishing wave carried out in the name of all the others.
An example from our own reporting: on 12 September 2026 we described how customers can check whether they were caught up in the Revolut data breach. According to the information available at the time, the exposed records covered copies of identity documents, verification selfies, IBANs and complete transaction histories. Not one of those fields is a password. That data set was nevertheless the basis for the personally addressed emails that circulated in the weeks that followed. We saw the same sequence in the summer of 2026 at several hardware wallet providers whose customer addresses escaped through a shipping contractor.
 The data set itself opens no wallet. It lends credibility to the message that tries to later on.
Typical signs of phishing: seven warning signals in the message itself
The warning signals below come from the cases that we and Germany's consumer advice centres encountered during 2026. None of them is proof on its own. Where two or more apply, treat the message as fraud.
Time pressure. A deadline of a few hours, a suspension said to be imminent, a payout that will otherwise lapse. Reputable providers allow weeks and send reminders. An action that works only through the link supplied. Genuine matters can always be dealt with by typing in the exchange's address yourself and logging in there. A request for secrets. Seed phrase, private key, password or the six digits from the authenticator app. More on this below. A withdrawal address you did not register yourself. If the email contains a wallet address to which you are supposed to transfer funds "for safekeeping", the matter is settled. An attachment. Crypto exchanges deliver tax reports and account statements through your logged-in account, not as a file in your inbox. The wrong email address in the recipient field. If the message arrives at an address under which you hold no account with that provider, it was sent from a purchased data set. An offer that is too good. Compensation for market losses, guaranteed returns, an airdrop for which you only have to sign one approval.What you can no longer use as a warning signal are spelling mistakes and a crooked layout. The messages of 2026 are linguistically clean and pixel-perfect in appearance. Anyone hunting for typos is looking in the wrong place. How far this now goes we described using a forged security warning that travelled through the manufacturer's genuine sending route and passed every technical authenticity check.
How to check a link for phishing without clicking it
The most reliable test costs you ten seconds and consists of not using the link at all. Open the exchange or the wallet app the way you always do, through your own bookmark or the installed app. If the same notice appears there, the email was genuine. If it does not, you have your answer without having risked anything.
If you still want to judge the link itself, look at the part immediately before the first single slash. That is the actual domain. Everything in front of it can be freely invented. An address of the form exchangename.security-login.example belongs to the operator of security-login.example, not to the exchange. Criminals also rely on similar-looking characters and on additional hyphens. On a phone, a long press on the link displays the destination address without opening it.
Two additions for everyday crypto use. First, a certificate and the padlock symbol in the browser say only that the connection is encrypted. Fraudulent websites have both. Second, if you are offered a wallet connection before you have read anything at all, close the page. Reputable providers request the connection only once you have triggered a specific action.
Which data a crypto exchange never requests by email
Three items are absolute. A reputable provider will not ask for them under any circumstances, neither by email, nor by telephone, nor in a support chat.
The seed phrase is your wallet's recovery phrase, usually twelve or twenty-four words in a fixed order. Every private key in your wallet can be recalculated from it. Whoever holds it holds your coins, immediately and without any further step. No manufacturer, no support desk and no public authority ever needs it. The private key is the cryptographic value with which a single address signs transactions; the same applies to it. The two-factor code from your authenticator app is valid for thirty seconds and exists precisely so that nobody but you knows it. Anyone asking you for it is sitting in front of your exchange's login form at that very moment.
A fourth item is trickier because it looks harmless: the screenshot as proof. A supposed support agent asks you to send a screenshot of your account or your wallet interface. From it, criminals read off balances, the networks you use and sometimes parts of addresses, and they build the next, still more credible message on that basis. Send no screenshots to anyone who contacted you first.
Fake support and wallet drainers: the schemes that turn leaked data into money
In practice, four fraud schemes grow out of a single data set, and you should keep them apart because each calls for a different defence.
The fake support desk. You receive a call or a message from your exchange's supposed security department. They know your name and your last deposit, and they cite a suspicious withdrawal that never happened. The remedy they offer is always the same: a code you are meant to read out, or a transfer to a "secure custody account". Hang up and call back on the number given on the provider's website.
The forged login page. The classic among phishing attacks. The link leads to a copy of the exchange, your input lands with the criminals, and they use it to log into the real account in real time. The only reliable protection is a second factor that cannot be passed on: a passkey or a security key tied to the genuine domain, which simply does not work on a copy.
The wallet drainer. This scheme targets your signature rather than your password. You land on a page, connect your wallet and confirm an approval. Smart contracts can be written so that this one approval permits an external contract to debit your tokens at any time. The wallet shows you no amount in the process, only a technical permission, and that is exactly what the criminals count on. Read which permission is being granted at every signature, and abort if you do not understand it.
The forged recall or replacement. Particularly popular after breaches at hardware providers. You are offered a free replacement for your device, and the new device arrives with a recovery phrase already prepared. A device that supplies you with a ready-made seed phrase has always been tampered with. A genuine wallet generates the phrase during setup, in front of you.
Crypto scams beyond phishing: what not to confuse the scheme with
Anyone who wants to spot crypto fraud should keep the common crypto scams apart, because each demands different countermeasures. Phishing takes away access you already hold. The other widespread schemes rely on you voluntarily paying in fresh money.
In investment fraud, crypto scammers build a relationship over weeks, usually through messengers or dating platforms, and lead the investor to an invented trading platform showing rising numbers. The first small payout works and creates trust; after that the sums demanded grow, and in the end the supposed provider asks for a fee before anything is paid out at all. In a rug pull, the team behind a freshly launched token disappears along with the funds collected. In the forged giveaway, a hijacked profile advertises a doubling of your money if you first send something to a named address.
The boundary between the two worlds is fluid, because the same tactics build on the same leaked data sets. Caution therefore includes one simple rule of thumb: in phishing, somebody wants something from you that you already have. In investment fraud, somebody promises you something that does not exist. Both methods end on the same blockchain, and in both cases the risk of total loss is real.
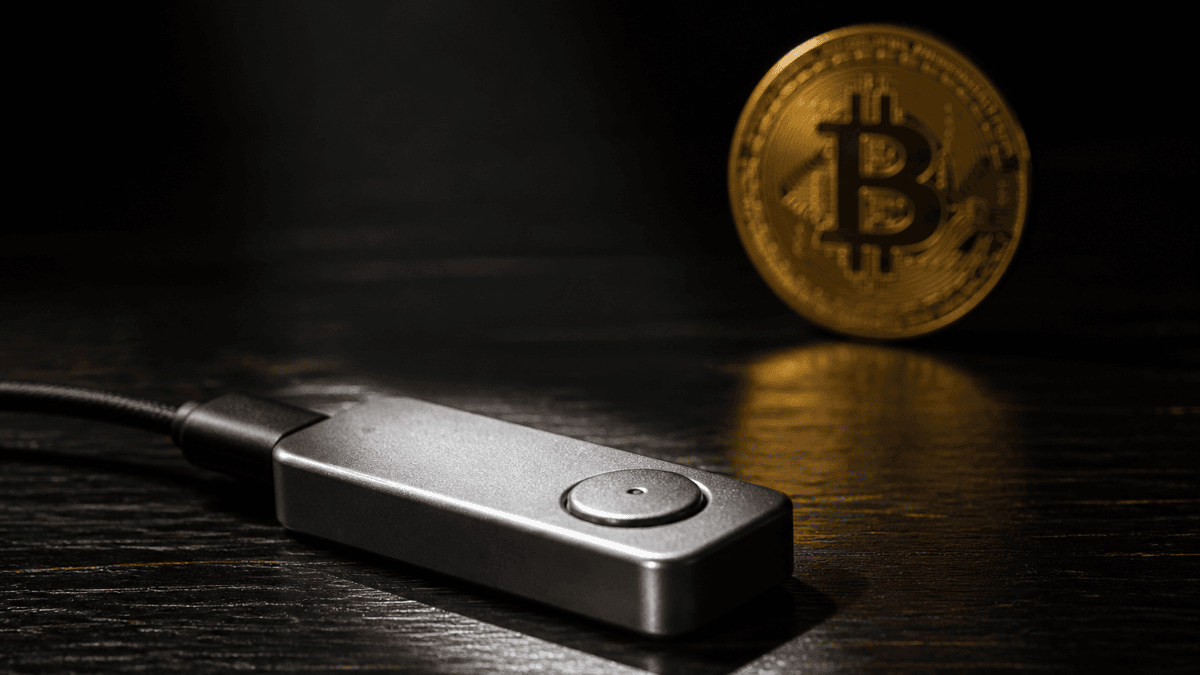 What has to be confirmed on the device cannot be triggered by a forged website alone.
Straight after the click: what counts in the first hour
Suppose it has happened. You clicked the link, entered data or signed an approval. The order of your steps then decides the outcome, not speed alone.
Cut off access. If you entered login credentials, change the exchange password from a different device and log out all active sessions. Depending on the provider, this function is called "manage devices" or "active sessions". Move the balance if a wallet is affected. If you signed an approval, changing a password will not help. Transfer the remaining holdings to a newly set up wallet with a fresh seed phrase. The old wallet counts as burned from that moment on. Revoke the permissions you granted. On networks with smart contracts you can withdraw existing approvals. That does not replace step two, but it prevents further outflows while you are still moving. Secure the evidence. Take screenshots of the message including the full headers, and note the transactions with times and addresses. Without those records a criminal complaint will not get far. File a complaint and inform the provider. The complaint goes to any police station, or online to the cybercrime reporting portal of your federal state. The provider can flag recipient addresses if the funds arrive at a regulated exchange.Part of setting expectations is the uncomfortable truth that the road to recovery is narrow. In practice it exists only where the stolen amounts arrive on a regulated platform with identity verification and are frozen there quickly enough. The longer you wait, the less likely that becomes.
Hardware wallet, passkeys and withdrawal allowlists: what devalues phishing for good
The most effective measures are those that render a successful fraud attempt inconsequential, instead of requiring you to spot it. Three of them are worthwhile for anyone holding more than a few hundred euros in cryptocurrencies.
A hardware wallet keeps the private key inside a device that never talks to the internet. Every transaction has to be confirmed on the device itself at the press of a button, and the display shows the recipient and the amount while you do so. A forged website can put on quite a show, yet it cannot press that button. Which devices differ in what respects, and what to look for when buying, we have set out in our hardware wallet comparison. Buy such a device exclusively from the manufacturer directly.
A passkey or a security key replaces the code from the authenticator app with a procedure tied to the genuine domain. On a rebuilt login page, no valid response is produced at all. That removes the most common scheme used against exchange accounts. Check your exchange's security settings to see whether it is offered, and set it up before you need it.
An allowlist of approved withdrawal addresses is the most underrated setting of all. Many crypto exchanges let you restrict withdrawals to addresses registered in advance, with a waiting period of one or two days for each new address. Even someone who takes over your account can then no longer reach your money immediately, and you have time to react.
For everyday use, some additions apply: a separate email address used only for crypto accounts, a password manager with its own password for each provider, and no crypto holdings mentioned in open social media profiles. Anyone not identifiable as a holder appears on fewer lists.
How to recognise a licensed provider, and why that helps against phishing
Since the European crypto regulation MiCA came into force, providers addressing retail customers in the EU require authorisation, granted and supervised in Germany by BaFin. For you this amounts to phishing protection for two reasons. First, the supervisor publishes the list of authorised firms; anyone absent from it is no candidate for your money. Second, authorised providers follow fixed rules for customer communication, which makes the number of permitted channels smaller and therefore easier to verify. Which obligations apply here we classify on an ongoing basis in our overview of the MiCA licence.
The scheme that attaches itself to this is already familiar from 2025: fraudsters pose as an unauthorised provider that supposedly has to tell its EU customers to withdraw their holdings. How such a demand can be checked we described in a separate guide to withdrawal demands after the MiCA deadline. The verification route is the same as in this article: never through the link in the message, always through access you have opened yourself.
Reporting phishing: consumer advice centres, providers and law enforcement
A report does little for you and a great deal for everyone else, because identified waves are blocked faster. Three addresses are worth the effort.
Germany's consumer advice centres operate a collective inbox for suspicious messages and publish the schemes they identify on an ongoing basis in their phishing radar. Looking there is worthwhile as a precaution too, whenever a message strikes you as odd. The provider in whose name the email was sent almost always has its own abuse reporting address; it is given in the help section. And the police accept complaints online through the federal states' cybercrime portals, including where no damage has yet occurred.
Crypto phishing: what to take away
Check your security settings today, not after the next breach. Switch the second factor to a passkey, activate the withdrawal allowlist, log out old sessions. Whether your provider offers any of this at all can be seen in our comparison of regulated crypto exchanges. Get the key out of the browser. Anyone holding positions over the long term should keep them on a device with physical confirmation. The differences and the prices are in the hardware wallet comparison. Separate everyday use from storage. A small software wallet for purchases and approvals, a separate address with no contract approvals whatsoever for your holdings. Which software wallets are suited to this is set out in the software wallet comparison.(As of September 20, 2026. This article is not investment advice. Prices and fee structures change; check the terms with the provider before you buy.)

 Bengali (Bangladesh) ·
 English (United States) ·